A familiar voice can be fake: design payment controls for deepfake fraud
Cyber insurance may support incident response, but a second-channel payment check is the control that can stop an AI-assisted transfer first.
Authenticity is no longer a control
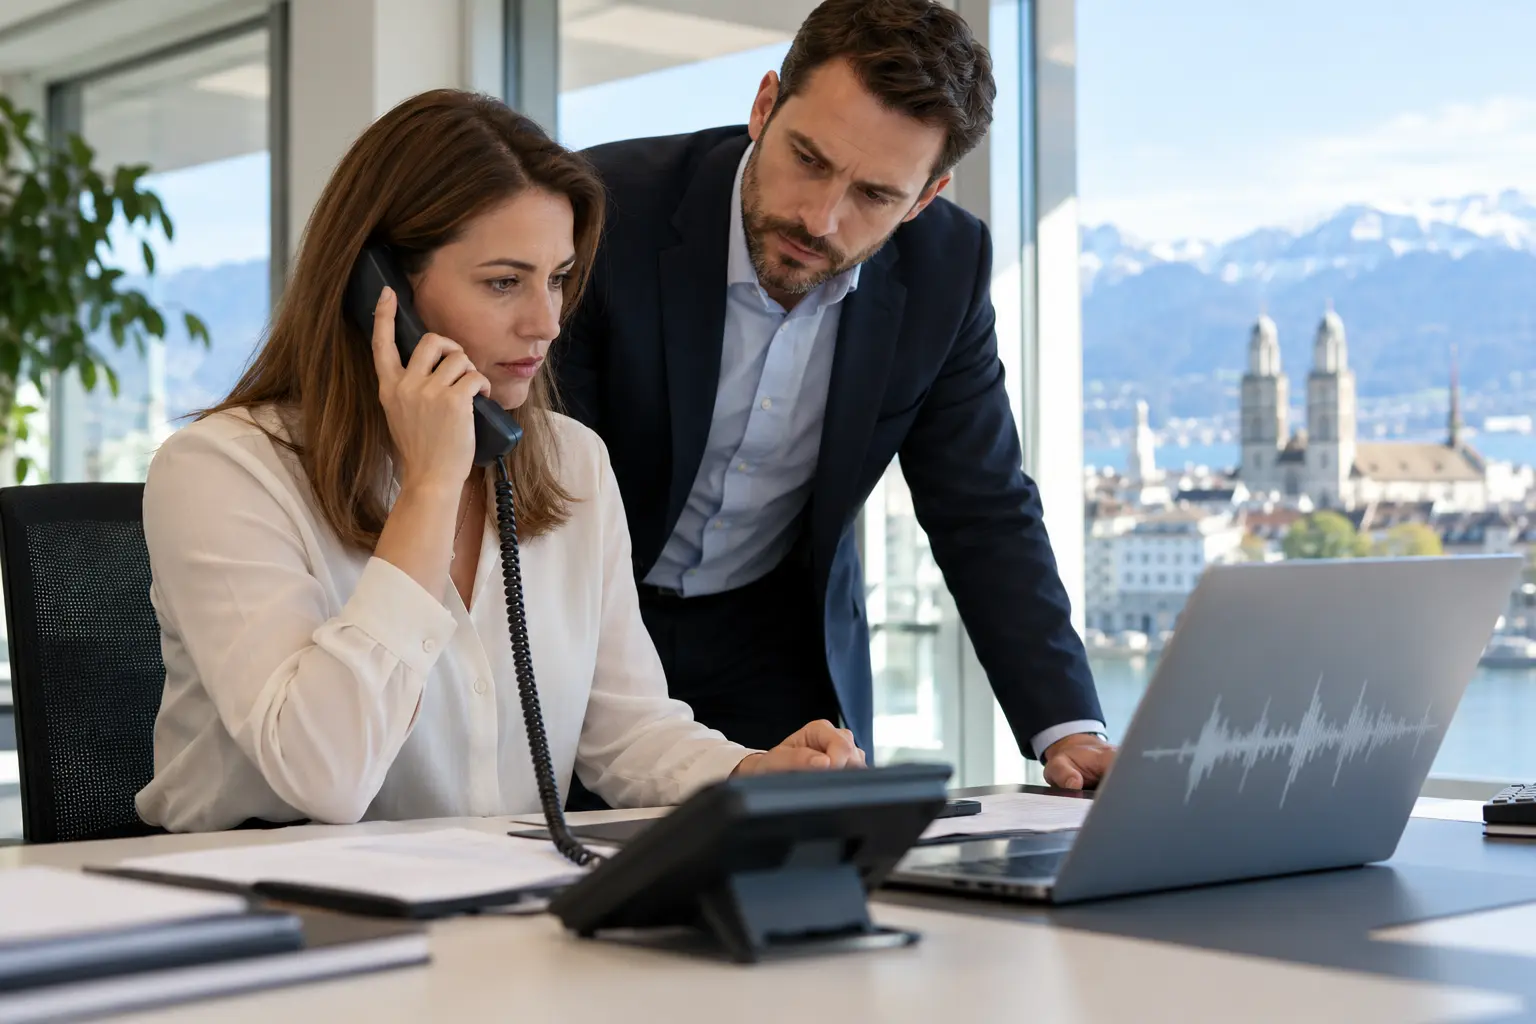
Generative tools can imitate a manager’s voice, face and writing style from public or stolen material. A call that sounds familiar, includes current business details and appears to come from the right number can still be fraudulent. The National Cyber Security Centre has warned that artificial intelligence makes convincing emails, images and voices easier to produce. Companies should therefore stop treating recognition as authorisation. The control question is not “Does this sound like the director?” but “Was this instruction verified through the approved process, by a person with the required authority, using a channel the requester did not choose during the call?”
Design friction at the point of payment
Require two-person approval for new beneficiaries, bank-detail changes and payments above a risk-based threshold. The second approver should inspect the source invoice and beneficiary history, not merely click. For urgent verbal requests, end the conversation and call a known number from the company directory or speak in person. A private challenge phrase can help, but it must be changed if exposed and should not replace approval. Configure bank limits, delayed release where practical and alerts for unusual destinations. Protect executive calendars, voice recordings and supplier contact data because they help attackers build a credible scenario.
A hypothetical Friday call
At 16:40, a finance clerk receives a video call that appears to show the managing director asking for CHF 86,000 to close an acquisition. The voice is convincing and the caller knows the lawyer’s name. The clerk invokes the policy, refuses to keep the call open as verification and phones the director’s saved mobile number. The real director knows nothing about the transfer. IT preserves the message headers and meeting link, blocks the account and reports the attempt. No money leaves. If funds had moved, immediate bank contact and incident notification would be crucial, but insurance coverage would depend on the social-engineering and funds-transfer clauses.
Coverage language can decide the loss
Cyber policies often fund forensic investigation, restoration, notification, crisis support and some business interruption. Direct theft of money may sit under a cyber-crime or crime extension and can have lower sublimits. A social-engineering clause may require that the company followed stated call-back or dual-approval controls. Voluntary transfer, employee dishonesty and pre-existing compromise can be treated separately. Broader cover costs more, but a limit is only useful if it matches the largest plausible payment and the wording fits the actual process. The insurer will not turn a weak control into a strong one after the event.
Rehearse a ten-minute verification
Select three realistic requests: a chief executive’s urgent transfer, a supplier changing IBAN and a payroll file sent from a compromised mailbox. Run them without warning, then measure whether staff use the directory, involve a second approver and preserve evidence. Update the payment procedure, delegated-authority list and insurer contacts. Tell staff they will be supported for stopping a senior person’s request while checking. If an attempt occurs, contact the bank through a trusted channel, isolate affected accounts, retain logs, inform the insurer and report to the competent authorities. No script guarantees safety, but repeatable verification removes urgency and familiarity from the attacker’s advantage.
Sources and further reading
Original Clearwise analysis. External reporting provides context; rules and contract terms must be verified with the competent authority or provider. Some press articles may require a subscription.
Apply this to your situation
Compare your actual documents and clarify what matters before making a commitment.
Request a free consultationGeneral guidance, not a binding quote or personalised legal, tax or investment advice. Examples are hypothetical and results are not guaranteed.